
CERT-In has told the researcher who reported the vulnerabilities that one of the reported flaws has been fixed, while the remaining issues are still being worked on. The Election Commission’s ECINET platform had been flagged to India’s cybersecurity agency CERT-In months before it came under scrutiny within the poll panel, documents accessed by NDTV show.
He also reported that some certificate-checking protections could be bypassed, that certain access tokens and sensitive information were stored without encryption, and that some applications used fixed encryption values. He further reported what he described as an authentication weakness in live cVIGIL infrastructure. These findings were reported by Adhikary.
NDTV reached out to the poll body but did not receive a response immediately. “CERT was the organisation I could report the problems to. One of the findings was rated critical by the researcher. He alleged that a live ECINET API could return personal information belonging to election officials without requiring them to authenticate. Another vulnerability concerned the way ECINET handled encrypted responses. Adhikary’s July report, however, contained several other findings. He alleged that parts of the ECINET mobile application contained encryption keys directly inside the app. The cybersecurity disclosure came before a separate controversy over how ECINET itself was functioning within the Election Commission.
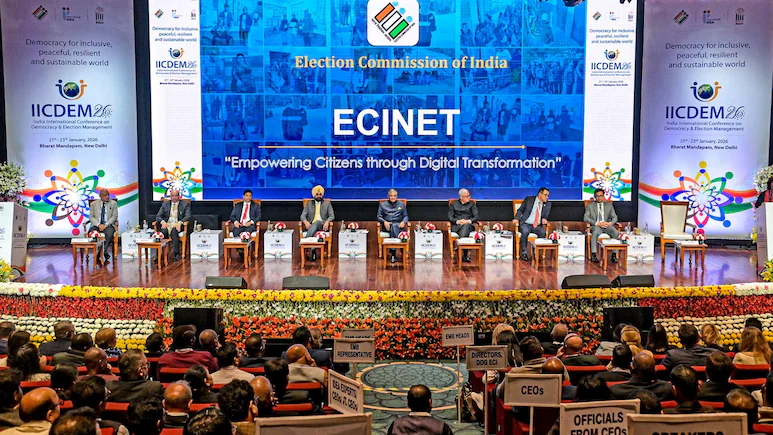
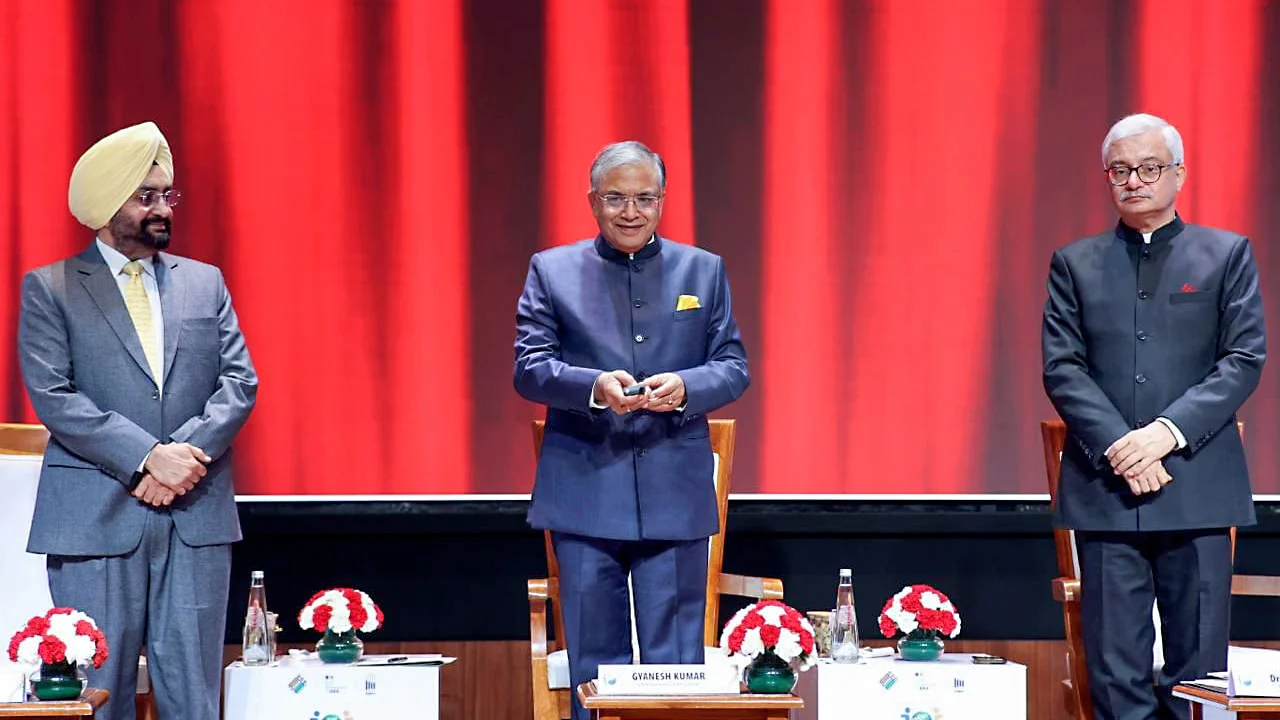
The response comes nearly three months after Adhikary’s July 8 disclosure to CERT-In and the Election Commission, in which he detailed vulnerabilities he said he had found in the Election Commission’s website and ECINET applications. The October 6 CERT-In communication confirms that the concerned organisation has said the hardcoded-key vulnerability has been fixed and that the remaining reported issues are under progress. ECINET was launched in January as a unified platform to bring together more than 40 election-related applications and services. Chief Election Commissioner Gyanesh Kumar and Election Commissioners Sukhbir Singh Sandhu and Vivek Joshi launch ECINET on January 22 For ECINET, the sequence is now clear: a cybersecurity researcher reported vulnerabilities to CERT-In in July; the Election Commission later faced internal questions over the functioning of its digital electoral infrastructure; the poll panel announced an independent review; and CERT-In has now said one of the reported security flaws has been fixed, with the others still under progress.
In an October 6 response to cybersecurity researcher Nisarga Adhikary , CERT-In said the vulnerability described as “Client-Side Static Response Encryption (Hardcoded AES Key)” had been fixed by the concerned organisation. The agency added that the other reported vulnerabilities were “under progress” and asked Adhikary to verify the fix at his end and confirm. “I reported the issue to the EC but received a boilerplate response,” Adhikary told NDTV. Adhikary said the interface returned information including the names, mobile numbers, designations and roles of election officials. He tested three officer-role combinations, received records in each case and said he stopped after those confirmations without downloading a larger dataset. The researcher also said the problem could potentially be repeated across different states, districts, Assembly constituencies and officer roles. The application contained a fixed encryption key in its publicly accessible code, according to Adhikary. He said the key could be recovered from the website’s JavaScript and used to decrypt API responses. This is the vulnerability that CERT-In has now said was fixed. Certain production endpoints accepted requests using a static token embedded in the application rather than an individual user’s login credentials, according to his report. He said he deliberately used invalid geographical information while testing so as not to retrieve real citizen or incident data.
During the Special Intensive Revision (SIR) of electoral rolls, Election Commissioners Sukhbir Singh Sandhu and Vivek Joshi reportedly raised concerns about aspects of the system, including access to electoral-roll databases and the way the software handled decisions that are legally assigned to election officials. Officials sought a mechanism to reverse such cases. The poll body has defended the declaration as part of the SIR exercise. The controversy eventually prompted the Election Commission to announce an independent review of ECINET, with a committee headed by a Senior Deputy Election Commissioner and including an independent technology expert from an IIT or IIIT.
There were also objections over an additional declaration incorporated into the online Form 6 , used for voter registration.
One issue arose in Goa, where voters initially flagged by the system for “logical discrepancies” were subsequently found eligible for inclusion. Sandhu called the change “unauthorised/illegal”, while Joshi questioned the modification of a statutory form without the prescribed process, according to The Indian Express report. CBSE disputed that its operational evaluation system had been compromised and said the portal identified by him was a testing environment.
Adhikary’s ECINET disclosure also follows his earlier reporting of alleged vulnerabilities in CBSE’s On-Screen Marking system.
